The platform behind the 24/7 shift

An AI SOC analyst and an AI vCISO, in every tenant.

Centeye watches every client 24/7 — catching the attacks point tools miss, correlating the noise down to what matters, and containing threats in minutes within the policy you set. Kavach runs the security operations — triage, correlation, staged response, verification. Argus documents every decision in reporting a client can act on. Round-the-clock coverage without staffing a night shift.

Policy-bound, reversible, audited — by design.

Why it matters

Attackers don’t care how small you are. They automate, so everyone’s a target.

The problem was never a shortage of tools — it’s having someone to run them around the clock. Most small businesses can’t hire a security analyst, let alone a team to cover nights and weekends. Centeye is that team, working 24/7 — for SMBs directly, and for the MSPs and MSSPs who protect them.

43%
of all cyberattacks target small business
— Verizon DBIR 2025
58%
of cyber claims are BEC + wire fraud
— Coalition 2026
$3.31M
average breach cost for orgs under 500 employees
— IBM Cost of a Breach 2025
61%
have no in-house security expertise of any kind
— ConnectWise 2025
What you get

Best-of-breed protection, without the sprawl.

Most businesses end up with seven disconnected tools throwing seven disconnected alerts. Centeye gives you the same coverage in one product — email, endpoint, identity, DNS-level visibility and the AI tools your team adopts — and ties every signal back to the user or device behind it. So a leaked credential, a suspicious login, a beacon and an encryption attempt read as one incident, not four you’ll never connect.

Why it wins

What changes when one team watches everything.

This isn’t a longer feature list — it’s a different way to be protected. Centeye is the security team any business can actually field, and every outcome below is something a pile of point tools structurally can’t deliver.

  • TEAM, NOT TOOL

    A full security team, not another product

    Kavach (AI SOC analyst) and Argus (AI vCISO) do the work of a SOC analyst, a fractional CISO and a pen-test firm — amplifying the team you have, or standing in for the one you can’t hire.

  • EDR / MDR · 24/7

    24/7 endpoint detection & response, managed

    Endpoint EDR delivered as MDR — Centeye watches every endpoint around the clock and, on anomaly, triggers a pre-emptive backup through your tenant backup solution so you keep a clean restore point.

  • ONE PLATFORM

    Four protections, one install

    Email, endpoint EDR & XDR, identity and the AI tools your team uses correlate in one platform — deployable without a security expert.

  • CROSS-SURFACE

    Correlation point tools miss

    A suspicious login and an endpoint beacon from the same user within an hour become one critical incident — not two ignored alerts.

  • NO CVSS

    Plain-English everything

    Every alert is AI-narrated as “what happened / what we did / what you do next” — built for the owner, not the analyst.

  • AUDITED · REVERSIBLE

    AI does the work, you stay in control

    You set the dial: low-risk containment can run on its own while higher-impact moves wait for approval — every action reversible and written to a tamper-evident log.

  • PRIVACY CONTRACT

    Zero-content email retention

    Mail is classified in flight; Centeye keeps the verdict and the metadata, not your inbox.

  • PROOF ON DEMAND

    Your security posture, always provable

    Centeye continuously evidences the controls you have in place and turns them into a signed, broker-ready posture report — no scramble before a renewal or an audit.

  • COMPOUNDING MOAT

    A detection moat that compounds

    A new attack on one tenant updates a privacy-preserving cross-tenant threat graph — counts, never tenant IDs — for everyone.

The team

What does an AI SOC analyst actually do here?

You bring the team on once. It never sleeps, never calls in sick, and never burns out on alerts. Kavach runs day-to-day security operations; Argus is the plain-English security lead who keeps the owner — and your MSP — in the loop on what happened and what to do next.

Kavach

Virtual SOC analyst

Amplifies your security team — and covers the shift you can't staff. Triages, correlates and remediates across every surface 24×7, so your people stop chasing alerts and focus on the calls that need judgment. You set the dial per action and per client: human-in-the-loop, autonomous within policy, or full auto-pilot from Watch through Auto-contain. Every step is reversible and written to a tamper-evident audit log.

  • Amplifies your team — and covers the 24×7 shift you can't staff
  • Correlates signals across surfaces into one entity-keyed kill-chain
  • Runs human-in-the-loop, autonomous, or auto-pilot — at the autonomy you set per action and per client
Argus

Virtual CSO · plain-English advisor

Translates posture and incidents into owner-readable language, drives insurance-readiness reporting, and runs live runbooks during active incidents — in-app or over email, Slack, Teams and SMS.

  • Answers “was that safe?” in plain English, in the channel you use
  • Writes the board-ready cyber-insurance readiness report
  • Drives step-by-step IR runbooks during a live incident
Inside Centeye

The real console — across every surface.

Continuous security posture and the live threat-intelligence picture, straight from the product.

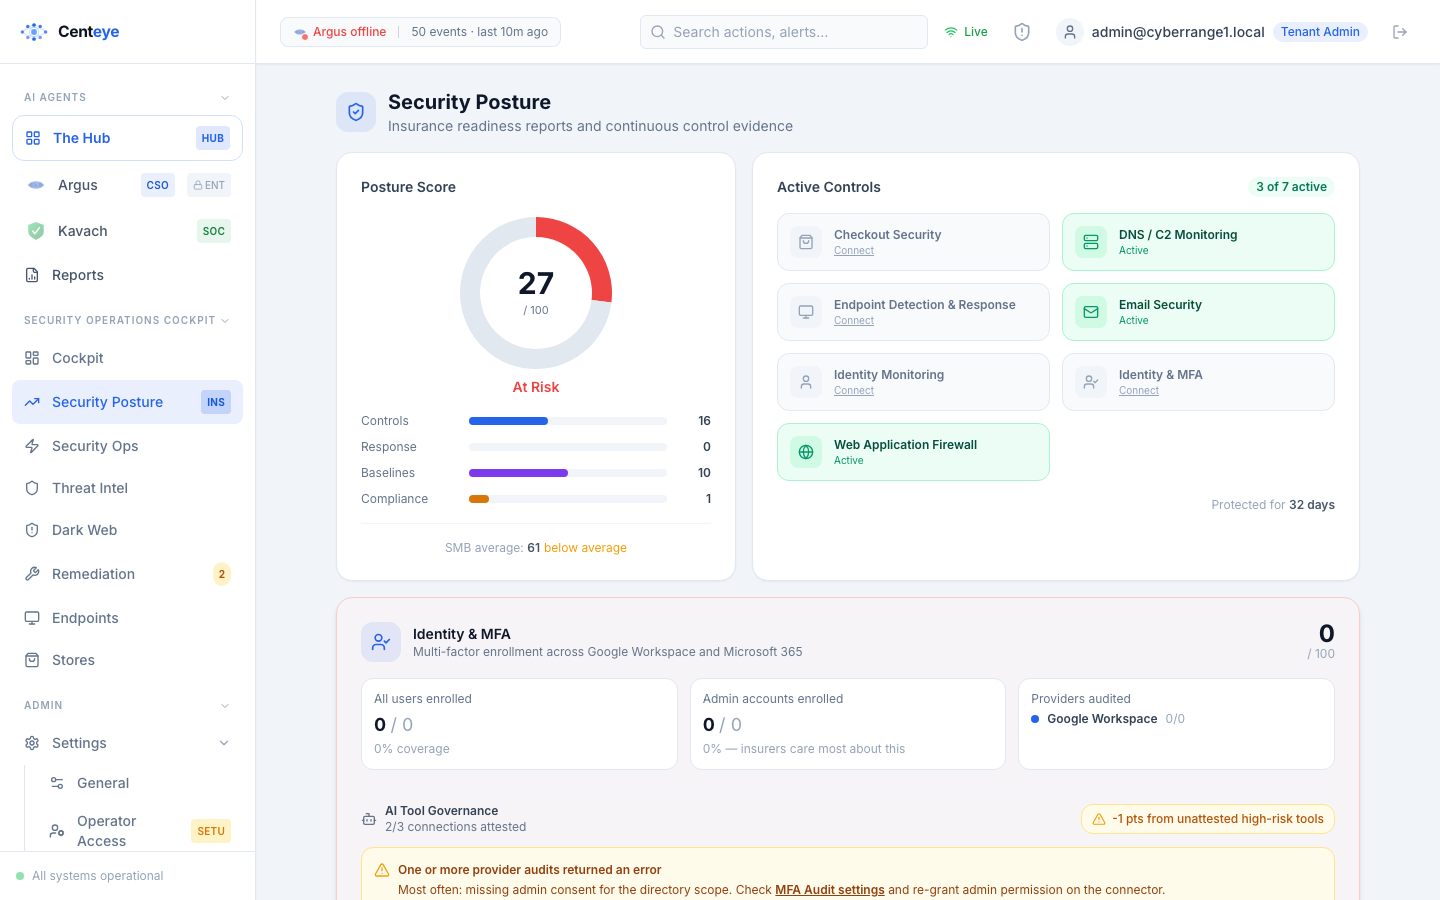
  • Centeye Security Posture — continuous control evidence across endpoint, email, web, DNS and identity, with a broker-ready posture report
    Continuous posture & control evidence Endpoint, email, web, DNS and identity coverage — provable in a signed, broker-ready report.
  • Centeye Threat Intelligence — indicators and campaigns mapped to your environment
    Threat intelligence, in context Indicators and campaigns mapped to what Centeye sees across your surfaces.
Human-in-the-loop → autonomous → auto-pilot

Graduated control — you set the dial.

Centeye amplifies the team you have — or covers the shift you can't staff — and lifts the alert overhead off your analysts. You decide how far they go on their own, per action and per client: keep it human-in-the-loop, let it run autonomous within policy, or hand the threats you trust to full auto-pilot. Every automated action is reversible and written to a tamper-evident audit log — fast response, human-grade judgment, with you in control.

  1. 0

    Watch

    Centeye detects and narrates. You stay informed — observe-only.

  2. 1

    Recommend

    Centeye surfaces the exact suggested action. You or your MSP decide.

  3. 2

    1-click Approve

    Centeye prepares the action; a human confirms with one tap and Centeye executes — security stays human-in-the-loop.

  4. 3

    Auto-contain

    For clear, dangerous, time-critical threats you trust, Centeye runs on auto-pilot — acts in minutes, then reports.

Built for the businesses that can’t hire a SOC — and the MSPs who serve them

Protect every client without staffing a 24/7 SOC.

One incident, not six alerts

Centeye connects signals from across your environment into a single incident — catching the attack a one-thing-at-a-time tool would let slip through.

Every client, one screen

See every client you manage from one place — cloud-first, fitting into the MSP tools you already run — with no separate SOC to stand up per account.

Posture you can prove

Continuously evidence the security controls you have in place and export a signed, broker-ready report — a retention and upsell lever, ready before the renewal call.

See your whole fleet, contained.

Get a guided demo of Centeye across your client tenants — and a plain-English read on where you stand today.